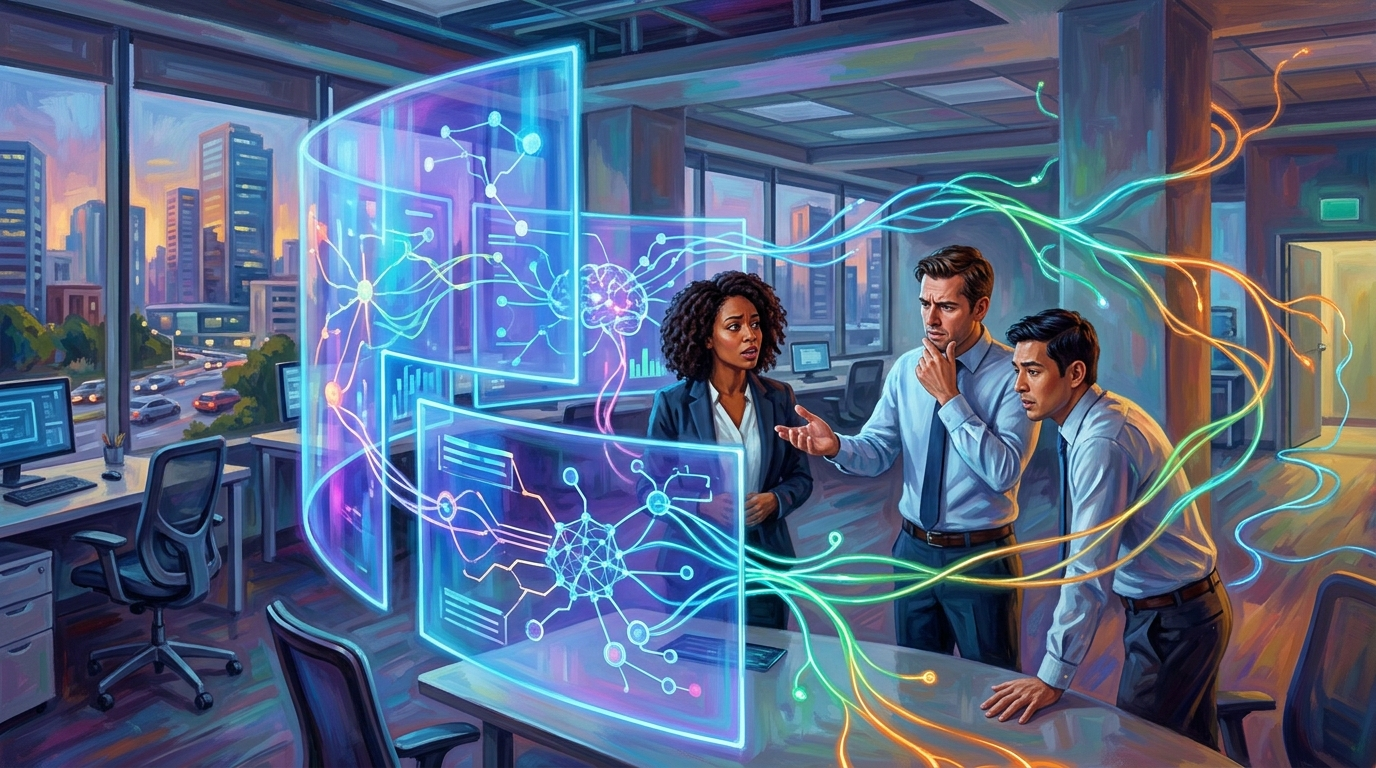
Enterprises adopting autonomous artificial intelligence face a growing governance problem as systems gain the ability to act without direct human approval.
Corporate AI policies have largely focused on tools that generate text, images, software code, and other content. Those rules may not cover systems that can make decisions, use company tools, or carry out a series of tasks.
The shift raises urgent questions about accountability, oversight, and risk. Companies must decide what an AI system can do, when people must intervene, and who is responsible when an automated action causes harm.
Governance Trails New AI Capabilities
Early corporate use of generative AI centered on productivity. Businesses tested whether models could summarize documents, draft messages, answer questions, or help employees write code.
That period shaped the first wave of governance controls. Policies often addressed inaccurate answers, invented information known as hallucinations, and the handling of private data.
“Much of the focus on generative AI has been on accuracy, hallucinations and productivity.”
Autonomous AI changes the risk calculation. A content generator usually produces material for a person to review. An autonomous system may instead select and execute the next step itself.
That difference can turn a flawed answer into a flawed action. Depending on its access, an AI agent could update records, contact customers, place orders, or trigger business processes.
Independent Action Demands New Controls
Traditional software follows defined instructions. Autonomous AI may interpret a goal, plan several steps, and adjust its conduct after receiving new information.
This flexibility can improve speed, but it also makes behavior harder to predict. Governance teams may struggle to assess every possible route an agent could take.
Companies evaluating these systems may need controls that address several basic issues:
- Which data, applications, and accounts an AI agent can access
- Which actions require human review or approval
- How decisions and tool use are recorded for audits
- How companies can stop, reverse, or contain harmful activity
Access limits are especially important. An agent with broad permissions can create greater operational and security risks than one restricted to a narrow task.
Accountability Becomes Harder to Assign
Independent action also complicates responsibility. Errors may involve the model provider, the company deploying it, the team configuring it, or the employee supervising it.
Clear ownership can reduce confusion after an incident. A business may assign named managers to each autonomous system and define escalation paths before deployment.
Human oversight remains one option, but it must be meaningful. Requiring approval for every minor step can erase productivity gains. Allowing unrestricted action can expose a company to avoidable losses.
A risk-based model offers a middle course. Low-impact tasks could proceed automatically, while financial, legal, safety, or customer-facing decisions receive closer review.
Testing Must Move Past Answer Quality
Accuracy tests alone cannot show whether an autonomous system is safe to operate. Enterprises also need to examine how agents choose tools, respond to failure, and behave under unexpected conditions.
Testing should reflect real workflows rather than isolated prompts. It should also measure whether safeguards work after software updates, new data access, or changes to an agent’s instructions.
The central challenge is no longer limited to whether AI produces reliable content. It now includes whether AI takes appropriate action. Enterprises that expand autonomy without updating governance may increase operational, legal, and security exposure. The next phase of adoption will depend on controls that preserve useful automation while keeping people responsible for its consequences.