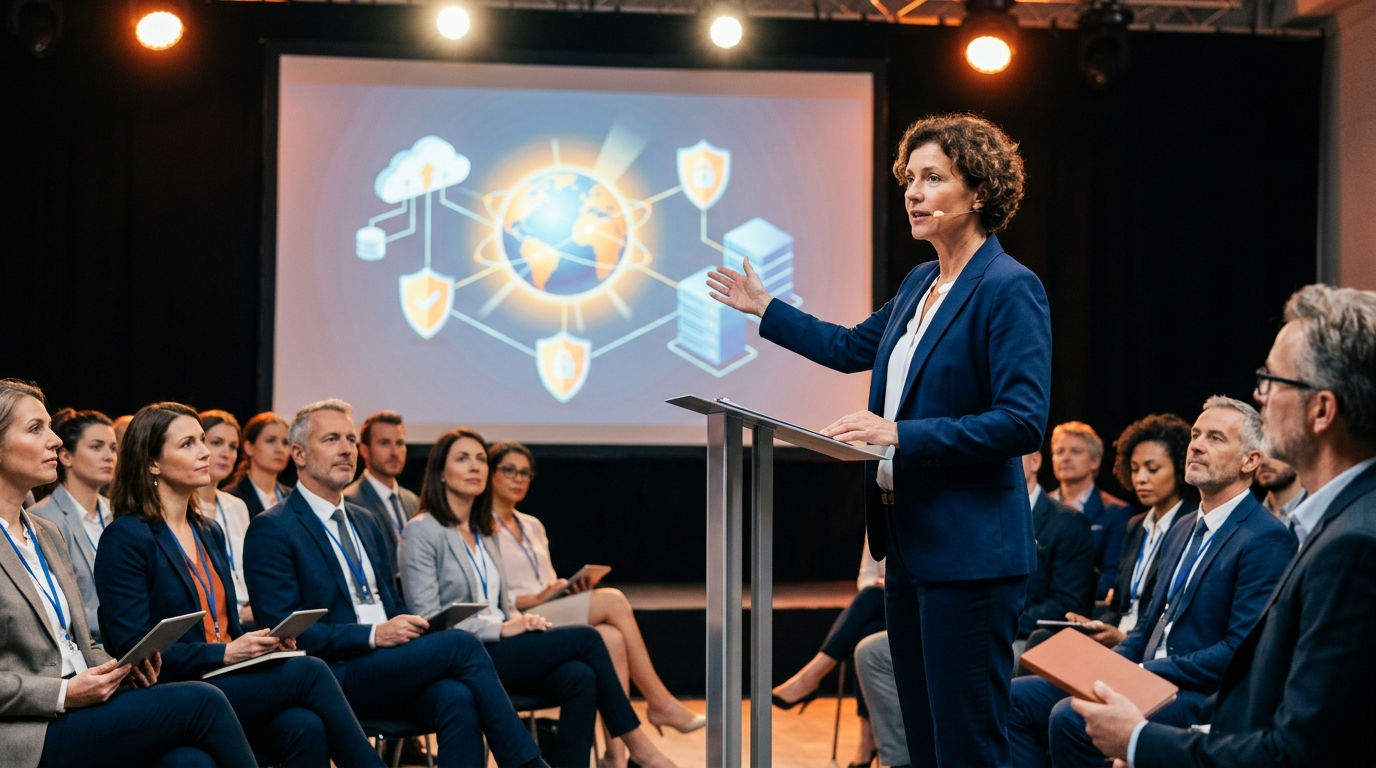
New IDC research from Cohere is placing sovereign AI at the center of enterprise technology planning. Chief AI Officer Joëlle Pineau is also outlining strategies for cloud security and data control, two concerns shaping corporate AI adoption.
The work addresses a growing question for organizations: how can they use artificial intelligence while keeping authority over sensitive information? The issue affects companies that rely on cloud services, operate across borders, or face strict privacy and security rules.
Why Sovereign AI Matters
Sovereign AI refers to systems designed to keep data, computing resources, and operational control within approved legal or geographic limits. The exact requirements differ by country, industry, and organization.
For enterprises, sovereignty is not limited to where data is stored. Leaders must also examine who can access information, which laws apply, and how AI providers process customer material.
These questions have gained weight as businesses add generative AI to internal search, customer service, software development, and document analysis. Such tools may handle confidential records or intellectual property.
The IDC research backed by Cohere addresses that tension. Its focus suggests that AI purchasing decisions are moving past model performance alone. Security, governance, and control now carry greater weight.
Cloud Security Requires Clear Controls
Pineau’s emphasis on enterprise cloud security points to the need for defined safeguards before AI systems enter routine use. Companies must know how information moves through a model and where copies may remain.
Key areas for review include:
- Data storage locations and applicable laws
- Access controls for staff, vendors, and administrators
- Policies governing whether customer data trains models
- Audit records, encryption, and incident response duties
Cloud deployment can give organizations speed and flexible computing capacity. It can also create dependence on outside providers. A sovereign approach seeks to preserve useful cloud access without surrendering control over critical assets.
That balance may require private cloud services, regional hosting, dedicated infrastructure, or systems installed within an organization’s own environment. Each choice carries different costs and security duties.
Data Control Becomes a Buying Test
Data control is also emerging as a practical test for AI vendors. Enterprise buyers need clear contract terms covering retention, deletion, access, and model training.
Those terms matter because AI systems often connect with company databases and document stores. Weak controls could expose regulated information, trade secrets, or customer records.
At the same time, tighter restrictions may raise deployment costs or slow projects. Business leaders must weigh those trade-offs against legal exposure and the damage caused by a security failure.
What Enterprises Should Watch
The attention from IDC and Cohere signals a wider shift in the AI market. Providers may face growing pressure to offer regional deployment, clearer audit tools, and stronger customer control.
Organizations should avoid treating sovereignty as a single technology purchase. It requires coordination among security teams, legal staff, data leaders, and business units.
Clear definitions will be important. A service described as sovereign may meet residency rules while still relying on foreign-operated software or support staff. Buyers must test such claims against their own risk standards.
The central takeaway is that enterprise AI strategy now depends as much on control as capability. As adoption expands, cloud security and data governance will help decide which systems earn trust, where they can operate, and which vendors win major contracts.